

Updated Nov-2025 Exam Engine or PDF for the NSK300 Tests Free Updated Today!
Ultimate Guide to Prepare NSK300 with Accurate PDF Questions
Netskope NSK300 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
NEW QUESTION # 35
Review the exhibit.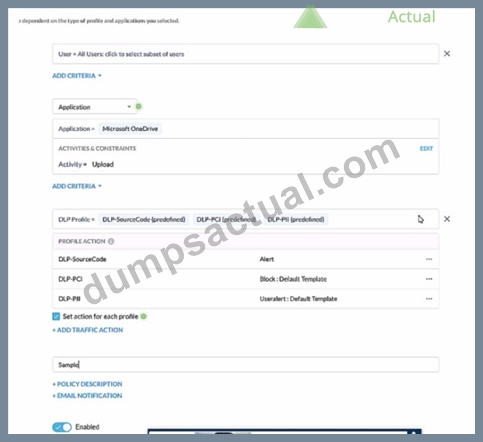
A user has attempted to upload a file to Microsoft OneDrive that contains source code with Pll and PCI data.
Referring to the exhibit, which statement Is correct?
- A. The user will be alerted and a single incident will be generated referencing the DLP-PII profile.
- B. The user will be blocked and a single Incident will be generated referencing the DLP-PCI profile.
- C. The user will be blocked and a separate incident will be generated for each of the matching DLP profiles.
- D. The user will be blocked and a single Incident will be generated referencing all of the matching DLP profiles
Answer: C
Explanation:
In the given scenario, a user is attempting to upload a file containing sensitive PII and PCI data to Microsoft OneDrive. The Netskope Security Cloud provides real-time data and threat protection when accessing cloud services, websites, and private apps from anywhere, on any device. Based on the exhibit provided, different DLP (Data Loss Prevention) profiles are triggered - DLP-SourceCode, DLP-PCI, and DLP-PII. Each of these profiles has specific actions associated with them; for instance, an alert is generated for Source Code while blocking actions are initiated for PCI and PII data. Since multiple DLP profiles are triggered due to the sensitive nature of the content in the file being uploaded, separate incidents will be generated for each matching profile ensuring comprehensive security coverage and incident reporting.
Reference:
Netskope Cloud Security
Netskope Resources
Netskope Documentation
NEW QUESTION # 36
Your company just had a new Netskope tenant provisioned and you are asked to create a secure tenant configuration. In this scenario, which two default settings should you change? {Choose two.)
- A. Change "Disallow concurrent logins by an Admin" to Enabled.
- B. Change Safe Search to Disabled
- C. Change Untrusted Root Certificate to Block.
- D. Change the No SNI setting to Block.
Answer: A,C
Explanation:
For a new Netskope tenant provisioned, to create a secure tenant configuration, you should consider changing the following default settings:
* B. Change Untrusted Root Certificate to Block: This setting will ensure that any traffic coming from an untrusted root certificate is blocked, which is a critical security measure to prevent man-in-the-middle attacks and other types of cyber threats1.
* D. Change "Disallow concurrent logins by an Admin" to Enabled: This setting will prevent multiple concurrent logins by the same admin account, which is an important security control to mitigate the risk of unauthorized access.If an admin's credentials are compromised, this setting will help limit the potential damage by ensuring that only one session can be active at a time1.
These changes are part of the recommended security hardening guidelines for Netskope tenants to enhance the overall security posture of the tenant environment.
The recommendations for changing default settings for a secure tenant configuration are based on Netskope' s security hardening guidelines, which provide detailed instructions on how to enhance the security of Netskope products and components deployed in customer environments1.
NEW QUESTION # 37
Users in your network are attempting to reach a website that has a self-signed certificate using a GRE tunnel to Netskope. They are currently being blocked by Netskope with an SSL error. How would you allow this traffic?
- A. Ensure that the users add the self-signed certificate to their local certificate store.
- B. Configure a Real-time Protection policy with the action set to Allow.
- C. Set the No SNI setting in Netskope to Bypass.
- D. Configure a Do Not Decrypt SSL Decryption rule to allow traffic to pass.
Answer: D
Explanation:
To allow traffic from a website with a self-signed certificate that is being blocked by Netskope with an SSL error, the correct action is to configure a Do Not Decrypt SSL Decryption rule. This rule will allow the traffic to pass without being decrypted, thus bypassing the SSL error caused by the self-signed certificate. This is a common practice for handling traffic from trusted internal applications or specific external sites that use self-signed certificates1.
NEW QUESTION # 38
Given the following:
Which result does this Skope IT query provide?
- A. The query returns all events of [email protected] downloading or uploading to or from the application "Amazon S3" using the Netskope Client.
- B. The query returns all events of everyone except [email protected] downloading or uploading to or from the site "Amazon S3" using the Netskope Client.
- C. The query returns all events of [email protected] downloading or uploading to or from the site 'Amazon S3" using the Netskope Client.
- D. The query returns all events of an IP address downloading or uploading to or from Amazon S3 using the Netskope Client.
Answer: C
Explanation:
The given Skope IT query specifies the following conditions:
User equals '[email protected]'
Access method equals 'Client'
Activity equals 'Download' or 'Upload'
Site equals 'Amazon S3'
The query combines these conditions using logical operators (AND and OR).
The result of this query will include all events where the specified user ('[email protected]') is either downloading or uploading data to or from the site 'Amazon S3' using the Netskope Client.
It does not include events related to other users or IP addresses. Reference:
Netskope Security Cloud Introductory Online Technical Training
Netskope Security Cloud Operation & Administration (NSCO&A) - Classroom Training
NEW QUESTION # 39
A hospital has a patient form that they share with their patients over Gmail. The blank form can be freely shared among anyone. However, if the form has any information filled out. the document is considered confidential.
Which rule type should be used in the DLP profile to match such a document?
- A. Use Exact Match with patient names
- B. Use predefined DLP Rule(s) that match the patient name.
- C. Use a dictionary rule for all your patient names.
- D. Use fingerprint classification.
Answer: D
Explanation:
The appropriate rule type to use in the DLP profile for a document that is considered confidential when filled out isfingerprint classification. Fingerprinting is a method used to identify and protect sensitive data within documents. It works by creating a digital fingerprint of a file, which can then be used to detect any copies or derivatives of that file.In this case, fingerprinting would allow the hospital to differentiate between the blank patient form, which can be freely shared, and the same form with patient information filled out, which is confidential1.
Netskope's DLP rules can contain elements such as predefined data identifiers, custom data identifiers, keyword identifiers from a dictionary file, RegEx expressions, and exact match criteria1.For this specific use case, fingerprint classification is the most effective method as it can accurately detect the presence of filled- out information in the forms, which is crucial for maintaining patient confidentiality as per HIPAA regulations1.
NEW QUESTION # 40
You are deploying the Netskope Client to Windows devices. The following command line would be used to install the client MSI file:
In this scenario, what is <token> referring to in the command line?
- A. the Netskope organization ID
- B. a Netskope user identifier
- C. the URL of the IdP used to authenticate the users
- D. a private token given to you by the SCCM administrator
Answer: A
Explanation:
In the context of deploying the Netskope Client to Windows devices, <token> in the command line refers to the Netskope organization ID. This is a unique identifier associated with your organization's account within the Netskope security cloud. It is used during the installation process to ensure that client devices are registered and managed under the correct organizational account, enabling appropriate security policies and configurations to be applied. Reference: The answer can be inferred from general knowledge about installing software clients and isn't directly available on Netskope's official resources.
NEW QUESTION # 41
A company wants to capture and maintain sensitive Pll data in a relational database to help their customers. There are many employees and contractors that need access to sensitive customer data to perform their duties The company wants to prevent the exfiltration of sensitive customer data by their employees and contractors.
In this scenario. what would satisfy this requirement?
- A. exact data match
- B. machine learning
- C. regular expression
- D. fingerprinting
Answer: D
Explanation:
Fingerprinting would satisfy the requirement to prevent the exfiltration of sensitive Personally Identifiable Information (PII) data by employees and contractors. Fingerprinting is a data protection technique that involves creating a unique digital representation of sensitive data. This allows for the detection of any exact or partial matches of the fingerprinted data leaving the company's environment, thereby preventing unauthorized data exfiltration. It is particularly effective in scenarios where multiple individuals require access to sensitive data, as it can protect against both inadvertent and malicious attempts to move data outside of authorized channels1.
NEW QUESTION # 42
Your CISO asks that you to provide a report with a visual representation of the top 10 applications (by number of objects) and their risk score. As the administrator, you decide to use a Sankey visualization in Advanced Analytics to represent the data in an efficient manner.
In this scenario, which two field types are required to produce a Sankey Tile in your report? {Choose two.)
- A. Period of Type
- B. Pivot Ranks
- C. Dimension
- D. Measure
Answer: C,D
Explanation: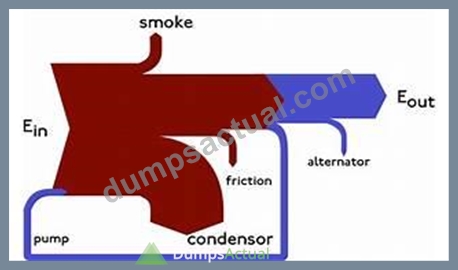
To produce a Sankey Tile in a report that visually represents the top 10 applications by number of objects and their risk score, you would need:
Dimension (A): This field type would be used to represent the nodes in the Sankey visualization, which could be the applications in this case1.
Measure (B): This field type would provide the weight of the links between the nodes, representing the number of objects or the risk score associated with each application1.
These two field types are essential for creating a Sankey visualization as they define the structure and flow of data between different stages or categories within the visualization.
NEW QUESTION # 43
Your customer is currently using Directory Importer with Active Directory (AD) to provision users to Nelskope. They have recently acquired three new companies (A. B. and C) and want to onboard users from the companies onto the NetsKope platform. Information about the companies is shown below.
- Company A uses Active Directory.
-- Company B uses Azure AD.
-- Company C uses Okta Universal Directory.
Which statement is correct in this scenario?
- A. Company A users cannot be provisioned to Netskope because the customer is already using AD Importer to import users from another Active Directory environment.
- B. Either Company B or Company C users cannot be provisioned because integration with only one SCIM solution is allowed.
- C. Users from Companies A. B, and C can be provisioned to Netskope by deploying additional AD Importers and integrating more than one SCIM solution.
- D. Users from Company B and Company C cannot be provisioned because the customer is already using AD Importer.
Answer: C
Explanation:
Users from Companies A, B, and C can indeed be provisioned to Netskope. Company A, which uses Active Directory, can continue to use the existing AD Importer. For Company B that uses Azure AD and Company C that uses Okta Universal Directory, integration with SCIM (System for Cross-domain Identity Management) solutions is possible.Netskope supports provisioning users from multiple directories, including Active Directory and cloud-based identity providers like Azure AD and Okta, by using additional AD Importers and integrating more than one SCIM solution12.
The correct approach for provisioning users from different companies that use various directory services is supported by Netskope's capabilities to integrate with multiple identity providers and directory services, as outlined in their documentation and community resources12.
NEW QUESTION # 44
You created a Real-time Protection policy that blocks all activities to non-corporate S3 buckets, but determine that the policy is too restrictive. Specifically, users are complaining that normal websites have stopped rendering properly.
How would you solve this problem?
- A. Create a Real-time Protection policy to allow the Download activity to the Amazon S3 application
- B. Create a Real-time Protection policy to allow the Download activity to the Cloud Storage category
- C. Create a Real-time Protection policy to allow the Browse activity to the Amazon S3 application.
- D. Create a Real-time Protection policy to allow the Browse activity to the Cloud Storage category
Answer: D
Explanation:
To solve the problem of normal websites not rendering properly due to a Real-time Protection policy that blocks all activities to non-corporate S3 buckets, the best solution is to create a Real-time Protection policy to allow the Browse activity to the Cloud Storage category. This approach will enable users to view content from various cloud storage services, including Amazon S3, without allowing full access to non-corporate S3 buckets. It's a more granular and less restrictive policy that allows necessary browsing activities while still maintaining control over the upload and download activities to non-corporate buckets1.
The Netskope Knowledge Portal provides information on how to configure Real-time Protection policies, including how to set up policies that allow certain activities while blocking others1. Additionally, the Netskope Community Forum offers insights into best practices for policy configuration to avoid overly restrictive rules that can impact normal web browsing
NEW QUESTION # 45
You have multiple networking clients running on an endpoint and client connectivity is a concern. You are configuring co-existence with a VPN solution in this scenario, what is recommended to prevent potential routing issues?
- A. Configure the VPN to full tunnel traffic and add an SSL Do Not Decrypt policy to the VPN configuration for all Netskope traffic.
- B. Configure the VPN to split tunnel traffic by adding the Netskope IP and Google DNS ranges and set to Exclude in the VPN configuration.
- C. Configure a Network Location with the VPN IP ranges and add it as a Steering Configuration exception.
- D. Modify the VPN to operate in full tunnel mode at Layer 3. so that the Netskope agent will always see the traffic first.
Answer: D
Explanation:
* To prevent potential routing issues and ensure that the Netskope agent consistently sees the traffic first, it is recommended to modify the VPN to operate in full tunnel mode at Layer 3.
* In full tunnel mode, all traffic from the endpoint is routed through the VPN, including traffic destined for Netskope. This ensures that the Netskope agent can inspect and apply policies to all traffic, regardless of the destination.
* Layer 3 full tunnel mode provides better visibility and control over the traffic flow, reducing the risk of routing conflicts or bypassing the Netskope inspection. References:
* The answer is based on general knowledge of VPN configurations and their impact on traffic routing.
NEW QUESTION # 46
Your organization's software deployment team did the initial install of the Netskope Client with SCCM. As the Netskope administrator, you will be responsible for all up-to-date upgrades of the client.
Which two actions would be required to accomplish this task9 (Choose two.)
- A. Set the installmode-IDP flag during the original Install.
- B. Set the autoupdate-on flag during the original Install.
- C. In the Client Configuration, set Upgrade Client Automatically to Latest Release.
- D. In the Client Configuration, set Upgrade Client Automatically to Specific Golden Release.
Answer: B,C
Explanation:
To ensure that the Netskope Client is always up-to-date with the latest upgrades, two actions are required.
First, in the Client Configuration, the administrator should set the option to Upgrade Client Automatically to Latest Release. This setting ensures that the client will automatically update to the most recent version available. Second, during the original installation of the Netskope Client, the autoupdate-on flag should be set.
This flag enables the auto-update feature, allowing the client to receive and apply updates as they are released.
The information is based on the Netskope Client deployment options and upgrade process as detailed in the Netskope Knowledge Portal
NEW QUESTION # 47
You are building an architecture plan to roll out Netskope for on-premises devices. You determine that tunnels are the best way to achieve this task due to a lack of support for explicit proxy in some instances and IPsec is the right type of tunnel to achieve the desired security and steering.
What are three valid elements that you must consider when using IPsec tunnels in this scenario? (Choose three.)
- A. the categories to be blocked
- B. Netskope Client behavior when on-premises
- C. cipher support on tunnel-initiating devices
- D. the impact of threat scanning performance
- E. bandwidth considerations
Answer: C,D,E
Explanation:
When using IPsec tunnels, especially in the context of deploying Netskope for on-premises devices, several factors must be considered to ensure a secure and efficient architecture:
Cipher support on tunnel-initiating devices (A): It is crucial to ensure that the devices initiating the IPsec tunnels support the ciphers used by Netskope. This compatibility is necessary for establishing secure connections.
Bandwidth considerations (B): The bandwidth available for the IPsec tunnels will affect the data throughput and performance of the connection. Adequate bandwidth must be allocated to handle the expected traffic without causing bottlenecks.
The impact of threat scanning performance (D): The performance of threat scanning can be affected by the encryption and decryption processes in IPsec tunnels. It is important to consider how the threat scanning capabilities will perform under the additional load of encrypted traffic.
These elements are essential for the successful implementation of IPsec tunnels in a Netskope architecture plan for on-premises devices12.
NEW QUESTION # 48
You deployed IPsec tunnels to steer on-premises traffic to Netskope. You are now experiencing problems with an application that had previously been working. In an attempt to solve the issue, you create a Steering Exception in the Netskope tenant tor that application: however, the problems are still occurring Which statement is correct in this scenario?
- A. Exceptions only work with IP address destinations
- B. You must deploy a PAC file to ensure the traffic is bypassed pre-tunnel
- C. Steering bypasses for IPsec tunnels must be applied at your edge network device.
- D. You must create a private application to steer Web application traffic to Netskope over an IPsec tunnel.
Answer: C
Explanation:
In the scenario where you have deployed IPsec tunnels to steer on-premises traffic to Netskope and are experiencing issues with an application, the correct statement isC: Steering bypasses for IPsec tunnels must be applied at your edge network device. This means that to effectively bypass the steering for a specific application, the configuration must be done on the network device that is establishing the IPsec tunnel, such as a firewall or router. This device controls the traffic before it enters the tunnel, so applying the bypass there ensures that the application's traffic does not get directed through the tunnel and can reach its destination directly.
The solution is based on standard practices for IPsec tunnel configuration and steering exceptions as described in Netskope's documentation on traffic steering and IPsec configuration12.
NEW QUESTION # 49
You want to integrate with a third-party DLP engine that requires ICAP. In this scenario, which Netskope platform component must be configured?
- A. Netskope Cloud Exchange
- B. Secure Forwarder
- C. Netskope Adapter
- D. On-Premises Log Parser (OPLP)
Answer: C
Explanation:
When integrating a third-party Data Loss Prevention (DLP) engine that requires ICAP, the Netskope platform component that must be configured is the Netskope Adapter. The Netskope Adapter is designed to facilitate the integration of Netskope with various third-party tools and services, including DLP engines that use ICAP for communication. By configuring the Netskope Adapter, you can ensure that the third-party DLP engine can communicate effectively with the Netskope platform to provide comprehensive data protection.
NEW QUESTION # 50
Your customer is currently using Directory Importer with Active Directory (AD) to provision users to Nelskope. They have recently acquired three new companies (A. B. and C) and want to onboard users from the companies onto the NetsKope platform. Information about the companies is shown below.
- Company A uses Active Directory.
-- Company B uses Azure AD.
-- Company C uses Okta Universal Directory.
Which statement is correct in this scenario?
- A. Company A users cannot be provisioned to Netskope because the customer is already using AD Importer to import users from another Active Directory environment.
- B. Either Company B or Company C users cannot be provisioned because integration with only one SCIM solution is allowed.
- C. Users from Companies A. B, and C can be provisioned to Netskope by deploying additional AD Importers and integrating more than one SCIM solution.
- D. Users from Company B and Company C cannot be provisioned because the customer is already using AD Importer.
Answer: C
Explanation:
Users from Companies A, B, and C can indeed be provisioned to Netskope. Company A, which uses Active Directory, can continue to use the existing AD Importer. For Company B that uses Azure AD and Company C that uses Okta Universal Directory, integration with SCIM (System for Cross-domain Identity Management) solutions is possible. Netskope supports provisioning users from multiple directories, including Active Directory and cloud-based identity providers like Azure AD and Okta, by using additional AD Importers and integrating more than one SCIM solution12.
NEW QUESTION # 51
A company has deployed Explicit Proxy over Tunnel (EPoT) for their VDI users They have configured Forward Proxy authentication using Okta Universal Directory They have also configured a number of Real-time Protection policies that block access to different Web categories for different AD groups so. for example, marketing users are blocked from accessing gambling sites. During User Acceptance Testing, they see inconsistent results where sometimes marketing users are able to access gambling sites and sometimes they are blocked as expected They are seeing this inconsistency based on who logs into the VDI server first.
What is causing this behavior?
- A. Forward Proxy is not configured to use the Cookie Surrogate
- B. Forward Proxy authentication is configured but not enabled.
- C. Forward Proxy is configured to use the Cookie Surrogate
- D. Forward Proxy is not configured to use the IP Surrogate
Answer: A
Explanation:
The inconsistent results observed during User Acceptance Testing (where marketing users sometimes access gambling sites and sometimes are blocked) are likely due to the configuration of the Forward Proxy.
Cookie Surrogate: The Cookie Surrogate is a mechanism used in Forward Proxy deployments to maintain user context across multiple requests. It ensures that user-specific policies are consistently applied even when multiple users share the same IP address (common in VDI environments).
Issue: If the Forward Proxy is not configured to use the Cookie Surrogate, it may lead to inconsistent behavior. When different users log into the VDI server, their requests may not be associated with their specific user context, resulting in varying policy enforcement.
Solution: Ensure that the Forward Proxy is properly configured to use the Cookie Surrogate, allowing consistent policy enforcement based on individual user identities. Reference:
Netskope Security Cloud Operation & Administration (NSCO&A) - Classroom Training Netskope Security Cloud Introductory Online Technical Training Netskope Architectural Advantage Features
NEW QUESTION # 52
You built a number of DLP profiles for different sensitive data types. If a file contains any of this sensitive data, you want to take the most restrictive policy action but also create incident details for all matching profiles.
Which statement is correct in this scenario?
- A. Create a Real-time Protection policy for each DLP profile; each matched profile will generate a unique DLP incident.
- B. Create a single Real-time Protection policy and include all of the DLP profiles; each matched profile will generate a unique DLP incident
- C. Create a single Real-time Protection policy and include all of the DLP profiles; all matched profiles will show up in a single DLP incident.
- D. Create a Real-time Protection policy for each DLP profile; all matched profiles will show up in a single DLP incident
Answer: C
Explanation:
When configuring a Real-time Protection policy with multiple DLP profiles, if the content matches multiple profiles, the policy performs the most restrictive action associated with the DLP profiles that match for that policy. The resulting incident lists all the profiles that matched along with their corresponding forensic information. This means that even though the most restrictive action is taken, details for all matching profiles are created and included in a single DLP incident12.
The explanation is based on the best practices and detailed descriptions provided in the Netskope Knowledge Portal and Community discussions, which outline the process of handling multiple DLP profile matches within a single Real-time Protection policy
NEW QUESTION # 53
You are implementing Netskope Cloud Exchange in your company lo include functionality provided by third- party partners. What would be a reason for using Netskope Cloud Risk Exchange in this scenario?
- A. to map multiple scores to a normalized range
- B. to ingest events and alerts from a Netskope tenant
- C. to feed SOC with detection and response services
- D. to automate service tickets from alerts of interest
Answer: D
Explanation:
The reason for using Netskope Cloud Risk Exchange in this scenario is toautomate service tickets from alerts of interest. Netskope Cloud Risk Exchange (CRE) is designed to ingest user, device, and application risk scores, creating a dashboard view of contributors to your company's overall risk score and trend. One of the key functionalities of CRE is to trigger risk-reducing actions through business rules that are tuned to a weighted score.Automating service tickets from alerts of interest is a part of this functionality, as it allows for the automatic creation of tickets in response to specific alerts, streamlining the process of addressing potential security issues12.
The use cases for Netskope Cloud Risk Exchange, including the automation of service tickets, can be found in the official Netskope resources1.Further information on how to integrate and utilize Netskope Cloud Risk Exchange for automating service tickets can be found in the Netskope Knowledge Portal3.
NEW QUESTION # 54
......
Pass Netskope With DumpsActual Exam Dumps: https://www.dumpsactual.com/NSK300-actualtests-dumps.html
Fully Updated NSK300 Dumps - 100% Same Q&A In Your Real Exam: https://drive.google.com/open?id=1RA88ua4KVD3e92sQ7N6e9BiHVYsn6NVV
